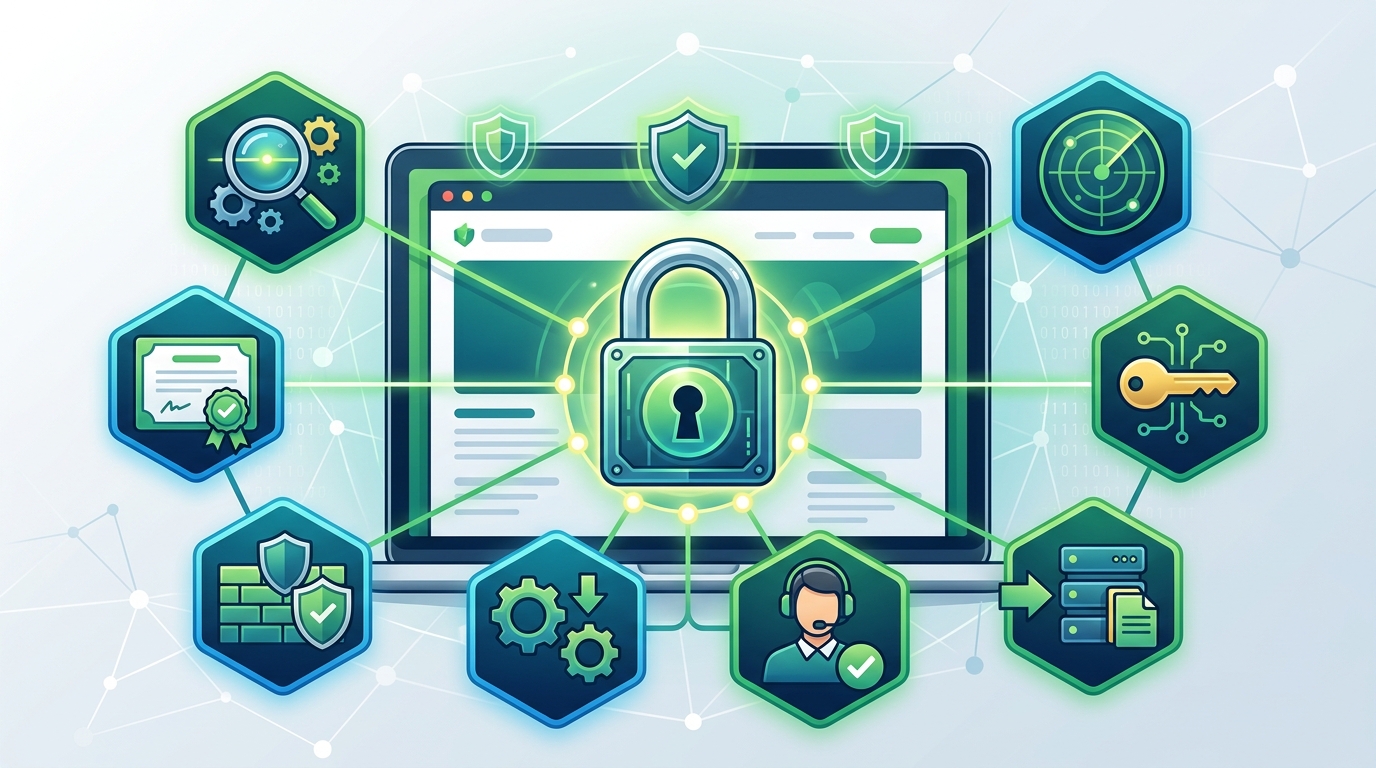
How to Secure Website: The Ultimate Guide to Online Safety
Do you know how to secure website platforms from malicious hackers? This question is more important today than ever before. Cyberattacks occur every single minute around the globe. Therefore, you must take proactive steps to protect your digital assets. A secure website builds trust with your visitors. It also protects your sensitive data from being stolen. In this comprehensive guide, we will explore the best practices for website security.
Hackers often target small and medium-sized businesses because they have weaker defenses. However, you can change that narrative today. By following these steps, you will create a digital fortress. For instance, implementing basic security protocols can stop 90% of automated attacks. Furthermore, search engines like Google reward secure websites with better rankings. Consequently, security is not just about safety; it is also about growth. Let us dive into the essential strategies you need.
1. How to Secure Website with an SSL Certificate
The first step in learning how to secure website data is using encryption. An SSL (Secure Sockets Layer) certificate is non-negotiable. It encrypts the data sent between your server and the user’s browser. This ensures that sensitive information like passwords and credit card numbers remains private. If you are operating in North America, looking for an SSL Canada provider is a smart move. They offer localized support and high-level encryption standards.
Using an SSL Certificate Canada service provides your users with peace of mind. They will see the padlock icon in their browser address bar. This icon signals that your site is legitimate and safe. Moreover, Google uses HTTPS as a ranking signal. Therefore, failing to install an SSL certificate will hurt your SEO efforts. Always choose a reputable provider to ensure your certificate is always up to date. You should never let your SSL expire, as this triggers scary warnings for your visitors.
2. Keep Your Software and CMS Updated
Software updates are the backbone of a secure website. Developers frequently release patches to fix security vulnerabilities. However, many website owners ignore these update notifications. This is a massive mistake. Hackers use automated tools to find sites running outdated software. Once they find a hole, they exploit it instantly. Therefore, you must update your CMS, plugins, and themes regularly. This simple habit significantly reduces your risk of a breach.
Furthermore, you should delete any software you no longer use. Old plugins and themes are often abandoned by their developers. These abandoned tools become easy targets for cybercriminals. Additionally, always download updates from official sources. Third-party or “nulled” plugins often contain hidden malware. By keeping your environment clean, you improve your site’s performance and security. Consistency is the key to maintaining a safe digital presence.
3. Use Strong Passwords and Multi-Factor Authentication
Weak passwords are a common entry point for hackers. Many people still use simple passwords like “123456” or “password.” Consequently, brute-force attacks are highly effective. You must use a combination of uppercase letters, lowercase letters, numbers, and symbols. Moreover, every user on your site should have a unique password. For instance, using a password manager can help you stay organized without sacrificing safety.
To add an extra layer of defense, enable Multi-Factor Authentication (MFA). MFA requires users to provide two or more verification factors. This might include a code sent to a mobile phone or a biometric scan. Even if a hacker steals your password, they cannot gain access without the second factor. Therefore, MFA is one of the most effective ways to prevent unauthorized access. Most modern platforms offer easy MFA integration for all users.
4. Implement a Web Application Firewall (WAF)
A Web Application Firewall (WAF) acts as a filter between your website and the internet. It examines incoming traffic and blocks malicious requests. For example, it can stop SQL injections and cross-site scripting (XSS) attacks. According to Wikipedia, a WAF is a specific type of application firewall. It focuses specifically on HTTP traffic to identify and neutralize threats before they reach your server.
Furthermore, many WAF services offer content delivery network (CDN) features. This improves your website speed while keeping it safe. You can choose between cloud-based firewalls or server-side solutions. Cloud-based firewalls are often easier to manage for beginners. They handle the heavy lifting of traffic filtering off-site. Consequently, your server resources remain dedicated to serving your legitimate customers. Investing in a quality WAF is a vital part of knowing how to secure website environments.
5. Schedule Regular Website Backups
No security system is 100% foolproof. Therefore, you must have a backup plan. A backup is a copy of your website stored in a separate location. If your site gets hacked or crashes, you can restore it quickly. For instance, you should back up your database and your files at least once a week. However, high-traffic sites may need daily or even hourly backups. Automated backup solutions make this process effortless for website owners.
Additionally, you should store your backups off-site. Storing backups on the same server as your website is risky. If the server is compromised, your backups might be deleted or encrypted as well. Use cloud storage services or a dedicated backup provider. Regularly test your backups to ensure they actually work. There is nothing worse than needing a backup and finding it corrupted. Preparation today prevents a total disaster tomorrow.
6. How to Secure Website by Limiting User Permissions and Roles
Not everyone who accesses your site needs full administrative rights. You should follow the principle of least privilege. This means giving users only the access they need to perform their jobs. For example, a guest blogger only needs “Editor” or “Author” permissions. They do not need access to your core security settings or server configurations. By limiting permissions, you reduce the potential damage if a user’s account is compromised.
Moreover, you should review your user list periodically. Remove accounts for former employees or contractors immediately. Inactive accounts are often targeted because no one is watching them. Additionally, ensure that your administrators use high-security settings. Education is also important. Teach your team about phishing and social engineering. Human error is often the weakest link in the security chain. Awareness creates a culture of safety within your organization.
7. Secure Your File Uploads
Allowing users to upload files to your server is a major security risk. Hackers can upload malicious scripts disguised as images or documents. Once the script is on your server, it can take full control of your site. Therefore, you must handle file uploads with extreme caution. For instance, you should always rename files upon upload to prevent overwriting. Furthermore, store uploaded files in a directory outside the web root if possible.
You should also implement file type validation. Only allow specific extensions like .jpg, .pdf, or .png. Additionally, use a malware scanner to check every uploaded file. Many security plugins offer this feature automatically. Finally, set strict file permissions on your server. Ensure that uploaded files do not have “execute” permissions. By controlling what comes onto your server, you maintain control over your entire website.
8. Choose a Secure Hosting Provider
Your hosting provider is the foundation of your website. If the host is insecure, your site will be too. Therefore, you must choose a host that prioritizes security. Look for providers that offer server-level firewalls and malware scanning. They should also provide automatic updates for the underlying server software. For instance, managed hosting providers often handle many security tasks for you. This allows you to focus on your content and business.
Furthermore, ask about their incident response plan. How do they handle a breach? Do they provide free site restoration? A good host will be transparent about their security measures. Additionally, avoid cheap shared hosting if security is a top priority. In a shared environment, one compromised site can sometimes affect others on the same server. Consequently, VPS or dedicated hosting is often a safer choice for growing businesses. Quality hosting is an investment in your peace of mind.
Conclusion: How to Secure Website Effectively
Learning how to secure website assets is an ongoing journey. The digital landscape is always changing. However, the fundamentals remain the same. Start with an SSL certificate to encrypt your data. Keep your software updated to close security holes. Use strong passwords and MFA to protect your accounts. Furthermore, implement a firewall and keep regular backups. These steps create a robust defense against most common threats.
Remember, security is not a one-time task. You must stay vigilant and monitor your site for suspicious activity. By being proactive, you protect your reputation and your customers. Furthermore, a secure site is a successful site. Do not wait for an attack to happen before you take action. Start implementing these strategies today and build a safer internet for everyone. Your future success depends on the security you establish now.